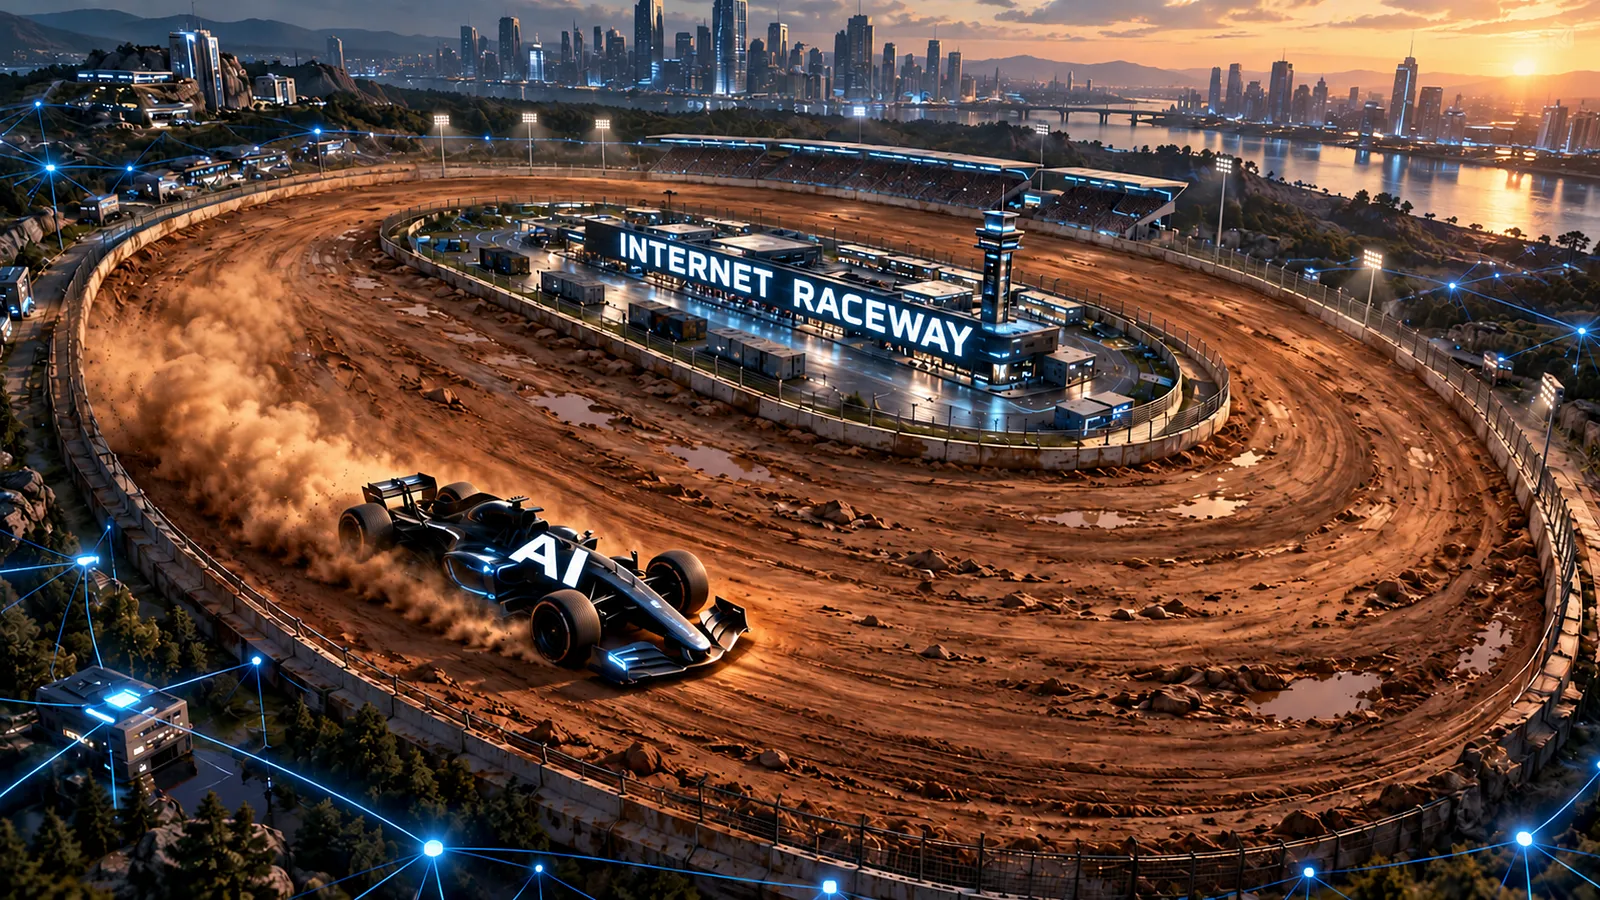
THE INTERNET is a dirt track in a formula one world
The Real Problem Isn’t Artificial Intelligence. It’s How We Protect the Internet.
By Ron Carter, Founder and CEO, 1AHEAD Technologies · October 2026
The Real Problem
Artificial intelligence (AI) is increasingly blamed for cyberattacks, identity theft, online fraud, and security breaches. But AI did not create most of these problems. It is simply exposing and exploiting weaknesses that have existed for decades.
The internet was developed long before today’s technology existed. Although its capabilities have advanced dramatically, many of the fundamental methods used to protect information and control access have remained largely unchanged.
The real problem isn’t that AI has become too powerful. It’s that our security systems haven’t become smart enough.
Why Traditional Security Is No Longer Enough
Today, we depend heavily on encryption, passwords, multifactor authentication (MFA), and other security measures to protect our information.
These protections remain important, but they have limitations that become increasingly apparent as AI advances.
Consider encryption. In simple terms, it can be compared to a sophisticated game of Scrabble, where information is mathematically scrambled and can only be restored using the correct key. Unlike an ordinary word game, modern encryption relies on extremely complex mathematics that remains highly resistant to attack when properly implemented.
However, encryption primarily protects information, not the decisions made about who should be permitted to access or use it. If an attacker obtains legitimate credentials or compromises an authorized system, encryption alone may not prevent misuse.
MFA presents a different challenge. It can be compared to a series of puzzles and responses designed to confirm someone’s identity. AI is making certain forms of deception, impersonation, and manipulation used to defeat these protections increasingly sophisticated.
The concern is not that AI can simply solve every encryption method or bypass every security challenge. It is that traditional security measures, even when combined, may fail to prevent unauthorized activity after access has been obtained.
Adding more locks to an outdated security system does not necessarily make that system smarter.
Data Centers: Highly Protected, but Not Invulnerable
Modern data centers represent some of the most sophisticated and secure environments in the world.
They benefit from high-speed fiber-optic networks, advanced encryption, physical security, redundant infrastructure, sophisticated monitoring, and multiple layers of cybersecurity protection.
These capabilities provide substantial protection against external threats.
However, a critical vulnerability remains.
Once an attacker successfully compromises a system, account, or privileged connection, the threat may spread rapidly through other accessible systems if additional safeguards fail to contain it.
In other words, even the strongest security perimeter cannot guarantee protection once an unauthorized party gains access.
This is particularly concerning because data centers support enormous volumes of financial transactions, business communications, government operations, and personal information.
The consequences of a successful intrusion can extend far beyond the original point of entry.
This exposes an important weakness in conventional security thinking: Preventing unauthorized entry is essential, but controlling what happens after entry is equally important.
A Better Way to Protect the Internet
Instead of relying primarily on stronger encryption, more complicated passwords, and additional authentication challenges, we should reconsider how permission to access information is granted and maintained.
Imagine a security system that does not simply ask, “Who are you?”
Instead, it continuously considers several important questions:
Are you authorized to access this information?
Are you using an approved device?
Are you permitted to perform this specific action?
Are you communicating with the correct destination?
Is your permission still valid at this exact moment?
This represents an important shift from simply verifying identity to controlling authorization.
Even when an attacker manages to obtain legitimate login credentials, those credentials should not automatically provide unrestricted access to other systems, information, or activities.
The objective is to make authorization specific, temporary, and continuously enforceable rather than assuming that successful authentication establishes ongoing trust.
Where 1AHEAD Technologies Offers a Different Approach
This is precisely the security challenge that 1AHEAD Technologies has invested years developing technology to address.
Supported by 20 issued U.S. patents, 1AHEAD’s intellectual property introduces an approach to access and authorization that can complement existing security infrastructure.
At the center of this architecture are intelligent, image-based digital credentials known as Non-Fungible Keys (NFKs).
Unlike conventional credentials, these keys are designed to support permissions that can be restricted to specific users, devices, destinations, activities, and periods of time.
They can also be changed, revoked, or allowed to expire automatically.
Consider the implications.
An individual might successfully enter a protected network, but that access would not necessarily provide permission to open another application, retrieve sensitive information, or initiate an unauthorized transaction.
Each protected activity could require its own valid authorization.
Instead of relying primarily on keeping intruders out, the architecture is designed to restrict what anyone can do, even after gaining access.
This introduces a potentially significant additional layer of protection against cyberattacks, compromised credentials, unauthorized transactions, and the misuse of legitimate access.
For data centers, the opportunity is particularly compelling.
Their existing infrastructure could support a more intelligent authorization layer, helping verify not only identities but also the legitimacy of individual access requests and transactions.
Such a system could reduce opportunities for attackers to move between protected resources, limit the damage caused by compromised credentials, and improve accountability.
These benefits would depend on proper implementation, integration, and independent security validation.
We Don’t Need to Rebuild the Internet
Perhaps the most important consideration is that meaningful improvements to internet security do not necessarily require replacing existing infrastructure.
The internet already provides extraordinary communication capabilities, processing power, and global connectivity.
Data centers already possess much of the infrastructure needed to support more advanced security services.
What remains underutilized is the opportunity to improve how access permissions are issued, verified, controlled, and withdrawn.
By introducing more intelligent authorization into existing environments, organizations could strengthen security without abandoning their current investments.
This approach also offers a practical response to the growing influence of AI.
Rather than attempting to develop security barriers that must continually become more difficult to defeat, we can make unauthorized actions harder to complete, even when conventional defenses are compromised.
The Opportunity We Are Overlooking
Artificial intelligence is not going away, nor should it.
Its ability to transform healthcare, education, financial services, transportation, and countless other industries is extraordinary.
But AI also exposes the limitations of security systems developed for a very different technological environment.
The answer cannot simply be more passwords, more encryption, and additional authentication challenges.
Those protections remain valuable, but they must be complemented by smarter decisions about authorization.
Security should no longer depend primarily on proving who someone is. It must also establish what that person or device is permitted to do, where, and for how long.
Final Thought
Artificial intelligence is accelerating the exploitation of weaknesses that existed long before AI became widely available.
Blaming AI distracts us from a more important opportunity: modernizing the architecture responsible for protecting our digital world.
Encryption, authentication, and traditional cybersecurity measures will remain essential. However, their effectiveness can be strengthened by a security architecture that continuously limits access to specifically authorized activities.
The next major advancement in cybersecurity may not come from making existing barriers more complicated, but from fundamentally improving how trust and permission are established.
1AHEAD Technologies has invested in developing intellectual property and technology directed toward this opportunity, with an architecture designed to complement existing infrastructure while addressing one of its most consequential limitations.
The future of internet security is not simply about keeping threats out. It is about ensuring that even when defenses are breached, unauthorized activity cannot proceed unchecked.
That is the architectural response 1AHEAD Technologies believes the industry has overlooked.
About the Author
Ron Carter is the Founder and CEO of 1AHEAD Technologies, inventor of the wireless video doorbell, and a member of the Forbes Technology Council. His pioneering innovation helped establish a global consumer-security industry. Today, he leads the development of next-generation security technologies supported by 20 issued U.S. patents.